Section: Data breaches · Last updated: October 26, 2026
This guide is based on the FTC Health Breach Notification Rule, 16 CFR Part 318, in the Electronic Code of Federal Regulations as of October 1, 2026, and the FTC’s final rule amending it (89 FR 47028, May 30, 2024, effective July 29, 2024). It is general information, not legal advice.
Many health and fitness apps are not covered by HIPAA, because they are not run by a hospital, a health plan or their contractors. That does not leave them without a breach notice duty. The Federal Trade Commission’s Health Breach Notification Rule fills part of that gap: it applies to vendors of personal health records and related entities that are not covered by HIPAA, and requires them to notify people, the FTC and, in some cases, the media.
The FTC amended the Rule in 2024. Its notice lists eight changes, including clarifying that the Rule covers developers of many health apps, that a “breach of security” includes unauthorized disclosures as well as data security breaches, and when the FTC itself must be told.
1. Who the Rule applies to
| Role in 16 CFR 318.2 | Meaning in the definition | Who it notifies |
|---|---|---|
| Vendor of personal health records | Offers or maintains a personal health record, and is not a HIPAA-covered entity or acting as a HIPAA business associate | Individuals, the FTC, and media where 500 or more residents of a State are affected |
| PHR related entity | Offers products or services through a PHR vendor’s website or online service, or accesses or sends health information to a personal health record | Same as a vendor |
| Third party service provider | Provides services to a vendor or related entity and holds or uses the unsecured health information as a result | The vendor or related entity it serves, which must acknowledge receipt |
A personal health record is an electronic record of identifiable health information that can draw information from multiple sources and is managed, shared and controlled by or primarily for the individual. The definition of “health care services or supplies” names online services, websites, mobile apps and internet-connected devices that track things such as fitness, sleep, diet, fertility, medications, vital signs, mental health or genetic information.
The Rule states that it does not apply to HIPAA-covered entities, or to any entity to the extent it acts as a HIPAA business associate. It reaches both foreign and domestic organisations that hold information about U.S. citizens or residents.
2. What counts as a breach
A breach of security is the acquisition of unsecured identifiable health information in a personal health record without the individual’s authorization. Two parts of the definition matter most:
- It includes unauthorized disclosure. The definition says a breach “includes an unauthorized acquisition” that occurs as a result of a data breach or an unauthorized disclosure. A breach does not need a hacker.
- Access is presumed to be acquisition. Unauthorized access is presumed to include unauthorized acquisition, unless the organisation has reliable evidence showing that acquisition did not happen or could not reasonably have happened.
“Unsecured” means the information was not protected by a technology or method specified in guidance from the Secretary of Health and Human Services. The FTC’s notice describes encryption that meets HHS specifications, with the keys kept separately from the data, as an example of secured information.
3. Deadlines
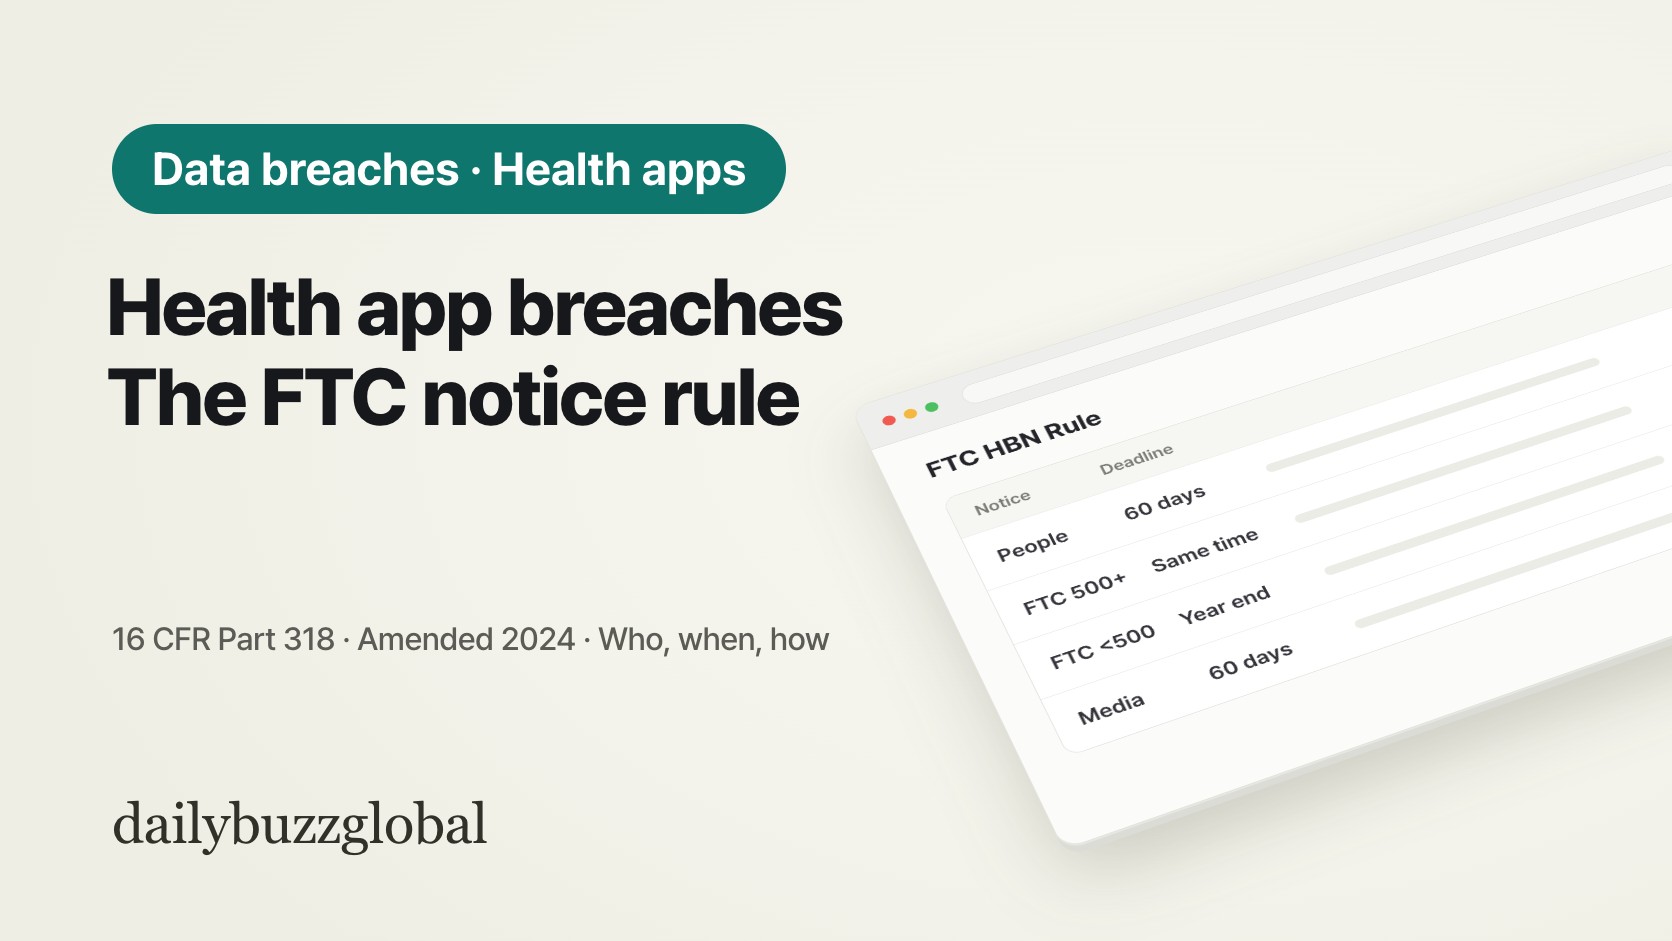
| Notice | Deadline in 318.4 |
|---|---|
| Affected individuals | Without unreasonable delay and no later than 60 calendar days after discovery |
| Media (500 or more residents of a State or jurisdiction) | Same 60-day limit |
| Service provider to its client | Same 60-day limit |
| FTC, 500 or more individuals | At the same time as the notice to individuals |
| FTC, fewer than 500 individuals | May be kept in a log and sent annually, no later than 60 calendar days after the end of the calendar year |
Before the 2024 amendments, the notice to the FTC for breaches of 500 or more people was due “as soon as possible and in no case later than ten business days” after discovery. It now goes with the notice to individuals.
A breach is treated as discovered on the first day it is known, or reasonably should have been known, to the organisation. Knowledge of any employee, officer or agent, other than the person committing the breach, counts. The organisation carries the burden of showing that every notice was made as required, including evidence for any delay. A law enforcement official can require a delay where notice would impede a criminal investigation or damage national security.
4. How people must be told, and what the notice says
Method (318.5). Written notice goes to the last known address. It may be sent by electronic mail if the person chose that as their primary method of contact. The Rule defines “electronic mail” as email combined with at least one of a text message, within-application messaging or an electronic banner, and such notices must be “clear and conspicuous”. If contact details for ten or more people are insufficient or out of date, substitute notice is required: a conspicuous posting on the home page for 90 days, or notice in major print or broadcast media, with a toll-free number active for at least 90 days.
Content (318.6). In plain language and to the extent possible:
- What happened, including the date of the breach and of its discovery, and the identity of any third parties that acquired the information, if known.
- The types of information involved. The Rule’s examples include health diagnosis or condition, lab results, medications, the person’s use of a health-related mobile app, and a device identifier in combination with another data element.
- Steps people should take to protect themselves.
- What the organisation is doing to investigate, mitigate harm and prevent further breaches.
- At least two ways to ask questions, chosen from a toll-free number, email, website, within-application contact or postal address.
5. Enforcement
Under 318.7, a violation is treated as a violation of a trade regulation rule under the FTC Act and is subject to civil penalties, adjusted for inflation. The FTC’s 2024 notice states that at the time of publication it had brought two enforcement actions under the Rule: against GoodRx Holdings, Inc. in 2023, which settled with a $1.5 million civil penalty, and against Easy Healthcare, Inc., developer of the ovulation-tracking app Premom.
FAQ
Q. My app shares data with an advertising partner without users’ permission. Is that a breach under this Rule?
The definition covers unauthorized acquisition resulting from an unauthorized disclosure, not only hacking. Whether a specific sharing arrangement is authorized depends on the facts, including what users agreed to.
Q. We are a HIPAA business associate for a hospital. Which rule applies?
The FTC Rule does not apply to an entity to the extent it acts as a business associate of a HIPAA-covered entity. Those activities fall under the HIPAA breach rules instead.
Q. Is an email alone enough to notify users?
Not under the Rule’s definition. Electronic notice means email together with at least one of a text message, in-app message or electronic banner, and only for people who chose electronic contact as their primary method.
Q. Do state breach laws still apply?
Section 318.1(b) says the Rule preempts State law as set out in section 13421 of the Recovery Act. How that interacts with a specific state law is a question for legal advice.
Official sources
- Electronic Code of Federal Regulations (ecfr.gov) — 16 CFR Part 318, Health Breach Notification Rule
- Federal Register, 89 FR 47028 (May 30, 2024) — Health Breach Notification Rule, final rule, Federal Trade Commission
- Federal Trade Commission (ftc.gov) — breach notice form and instructions referenced in 318.5(c)
This article is general information and not legal advice. Whether an app or service is covered depends on what it does and who it works for; check the current rule text and FTC guidance.